
2. Our Approach to Bioresilience: Isomorphic Labs and Google DeepMind (deepmind.google)
3. Steam Machine: Between 12k and 15k Units Sold per week (boilingsteam.com)
Steam Machine: Between 12k and 15k Sold per week
4. The Isomorphic Labs Drug Design Engine unlocks a new frontier beyond AlphaFold (www.isomorphiclabs.com)

5. Qubes OS Security in the Public Record (arxiv.org)
Qubes OS is a revealing case for security measurement because its architecture makes component boundaries security-relevant. We present a protocol-driven longitudinal analysis of 109 public Qubes Security Bulletins (QSBs, 2011--2025), the official Qubes-maintained Xen Security Advisory (XSA) tracker, and a secondary vulnerability-event sensitivity series. The study measures the public advisory record rather than latent vulnerability incidence or realized compromise. The methodology combines audited deterministic component attribution, change-point analysis, overdispersion checks, severity-proxy weighting, censoring sensitivity, documentary latency lower bounds, and baseline-aware evaluation of vulnerability discovery models (VDMs).
The results show persistent upstream dependence in that public record. On the official tracker, 113 of 464 XSAs affect Qubes; under primary labeling, 87 of 109 QSBs (79.8\%) are attributable to Xen, CPU/microarchitectural, or other upstream components rather than Qubes-core logic, with similar results under weighted views. Change-point analyses identify 2015Q1 as the dominant break in the quarterly advisory series, while post-2018 annual disclosure rates are statistically flat. Poisson inferences are stable under dispersion diagnostics and negative-binomial sensitivity checks. The attribution codebook performs well in a stratified 30-QSB audit, and S-shaped VDMs fit descriptively but do not significantly outperform a rolling-mean baseline in short-horizon forecasts.
Overall, the Qubes public advisory record appears stable, but not quiet: disclosure activity plateaus at a higher level than in the earliest years, while the observed burden remains concentrated in upstream trust anchors.
6. Stenchill: 3D Printable Solder Paste Stencil Generator (www.stenchill.com)
Free DIY tool to generate 3D-printable solder paste stencils from Gerber files. Convert Gerber to STL/3MF for FDM printing. Compatible with KiCad, Eagle, Altium.
7. Tech note: making your own V-I plots at home (lcamtuf.substack.com)
9. Co-evolution of self-replication and function in a digital primordial soup (arxiv.org)
While traditional evolutionary algorithms hard-code reproduction, self-replication can emerge spontaneously within digital ``primordial soups''. This paper investigates the co-evolution of this emergent self-replication alongside problem-solving capabilities. We initialize a population of random 32-byte Z80 assembly programs, requiring self-replication to arise purely through random assembly-level mutations and pairwise program interactions. To link these behaviors, we introduce a task-based validation step: correctly evaluating a polynomial raises a program's interaction probability above a baseline rate. Our experiments yield four primary findings. First, self-replication and mathematical problem-solving successfully co-evolve from initial randomness. Second, the pressure to compute accelerates the emergence of compact, robust reproductive architectures that preserve memory for task execution. Third, applying metabolic constraints increases the likelihood that programs evolve conditional halting, terminating early during validation while bypassing the halt during interaction to execute block-copy replication. Finally, when programs are partitioned into spatial task niches, spontaneous self-replication generates an emergent learning curriculum, utilizing simple solutions as stepping stones toward complex polynomials. Altogether, these results demonstrate an interactive feedback loop: environmental task demands actively shape the physical architecture of self-replication, while spontaneous replication alters the evolutionary trajectory of functional problem-solving.
11. An Update on Igalia's Layer Based SVG Engine in WebKit (Reducing Layer Overhead) (blogs.igalia.com)
Conditional layer creation in the layer based SVG engine
12. Moonstone: Modern, cross-platform Lua runtime and package manager written in Zig (moonstone.sh)
Moonstone — the modern, content-addressed package manager and deterministic environment orchestrator for Lua.
13. Judge a book by its first pages (uncovered.ink)
Read first pages blind. No cover, no name, no hype. Find out what you actually fall for.
14. In-toto: A framework to secure the integrity of software supply chains (in-toto.io)
A framework to secure the integrity of software supply chains
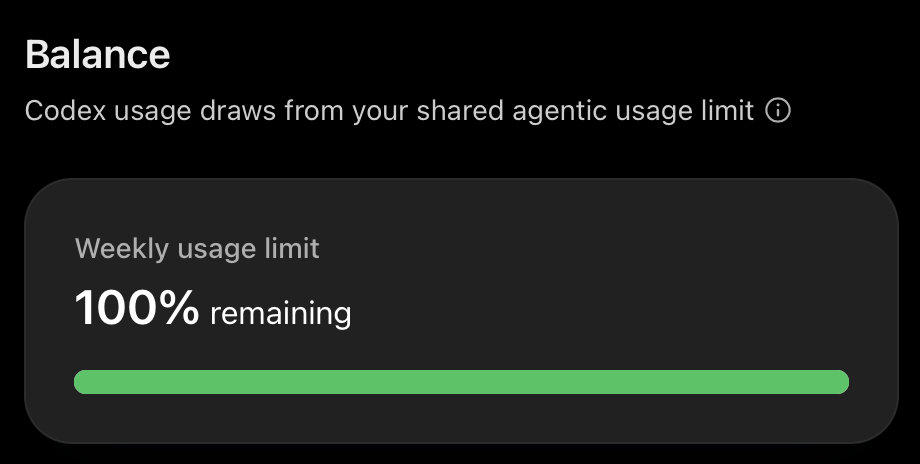
15. What's the deal with all the random weekly quota resets for agents lately? (minimaxir.com)
I’m going to be the weirdo who complains about literally getting free stuff.
16. Waldi: A quiet place to write, and to be read (github.com)
A quiet place to write, and to be read. Contribute to waaldev/waldi development by creating an account on GitHub.
17. Real-Time LuaTeX: Recompiling Large Documents in 1ms [pdf] (www.tug.org)
18. Porting nanochat to a TPU: what carries over from PyTorch, and what breaks (github.com)
Karpathy's nanochat normally runs on an 8×H100 GPU node, and several ports of it to JAX already exist. Among them, my aim was to keep the config and architecture as close to nanochat as possible (p...

19. No link between acetaminophen use during pregnancy and adverse birth outcomes (sph.unc.edu)
July 10, 2026 There is no statistically significant evidence that taking acetaminophen during pregnancy has a negative impact on how early a child is born or a child’s weight at birth, according to a new study led by Gillings School researchers.
20. Shipping OpenStrike: A Counter-Strike-Shaped FPS on a 2004 Handheld (pocketjs.dev)
OpenStrike is out — classic BSP maps, bots, tracers, and a Solid JSX HUD holding a locked 60 FPS on a real Sony PSP: 333 MHz, 32 MB, no shaders. A field guide for JavaScript developers to how it works: rules and HUD in TypeScript on QuickJS, a bundler for 1999

21. Mac gaming is finally getting the overpowered upgrade it deserves (www.macworld.com)
Game Porting Toolkit 4 beta is the clearest sign that gaming is becoming a priority for Apple.
22. Funny item co-occurrences in 3.2M Instacart orders (rogerdickey.com)
The strangest things people buy at the grocery store
23. A grumpy screed about AI in software engineering (sam.sutch.net)
A post about how AI slop has completely ovetaken software engineering.
24. Battery packs: Let's talk about crates, baby (smallcultfollowing.com)
25. SpaceX and the myth of independent Wall St research (www.ft.com)
26. Show HN: Get alerts for good seats at 70mm IMAX showings of The Odyssey (imaxxing.io)
Get frame mogged. I watch US 70mm IMAX seat maps and alert you when good seats for The Odyssey open up.
27. The Fermi Paradox, Percolation, and Inbreeding (reactormag.com)
What do cheetahs and genetic bottlenecks have to do with interstellar colonization? Glad you asked...
29. Revisiting Yliluoma's ordered dither algorithm (30fps.net)
30. "Disk Not Ejected Properly": What It Means (bombich.com)
That "Disk Not Ejected Properly" macOS alert isn't always your fault. Learn what's really happening and how to tell a flaky cable from failing hardware.