
Telegram Desktop vulnerability allowed any user's file to be stolen
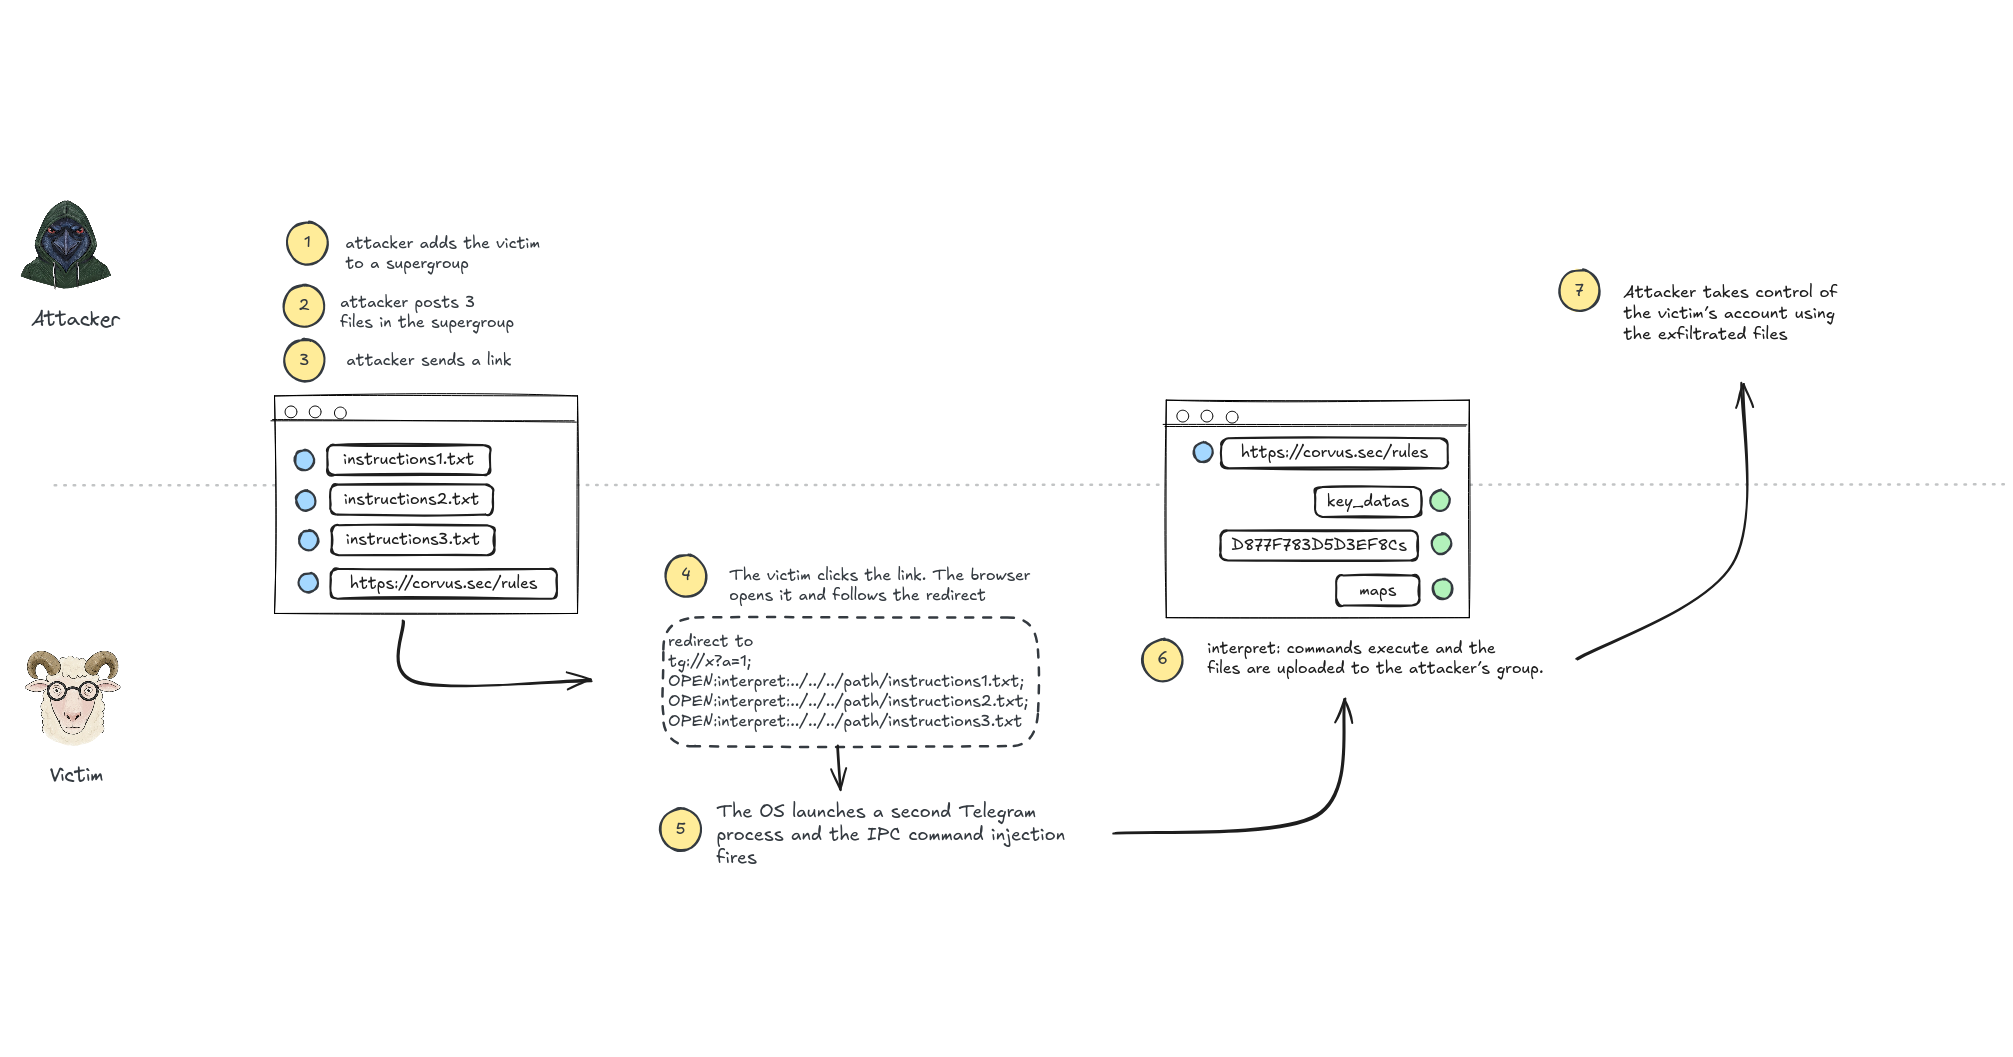
An unescaped separator in Telegram Desktop’s single-instance IPC lets one clicked link read arbitrary files off the disk and send them to the attacker, session files included.
Summary
A vulnerability in Telegram Desktop could allow attackers to steal arbitrary files from a user’s device simply by clicking a link. This security flaw raises significant concerns about user data privacy and protection on the platform.
Comments (317 of ) ⌛