
Show HN: GeoSpoof – your VPN hides your IP, but the browser leaks your location
Original Text
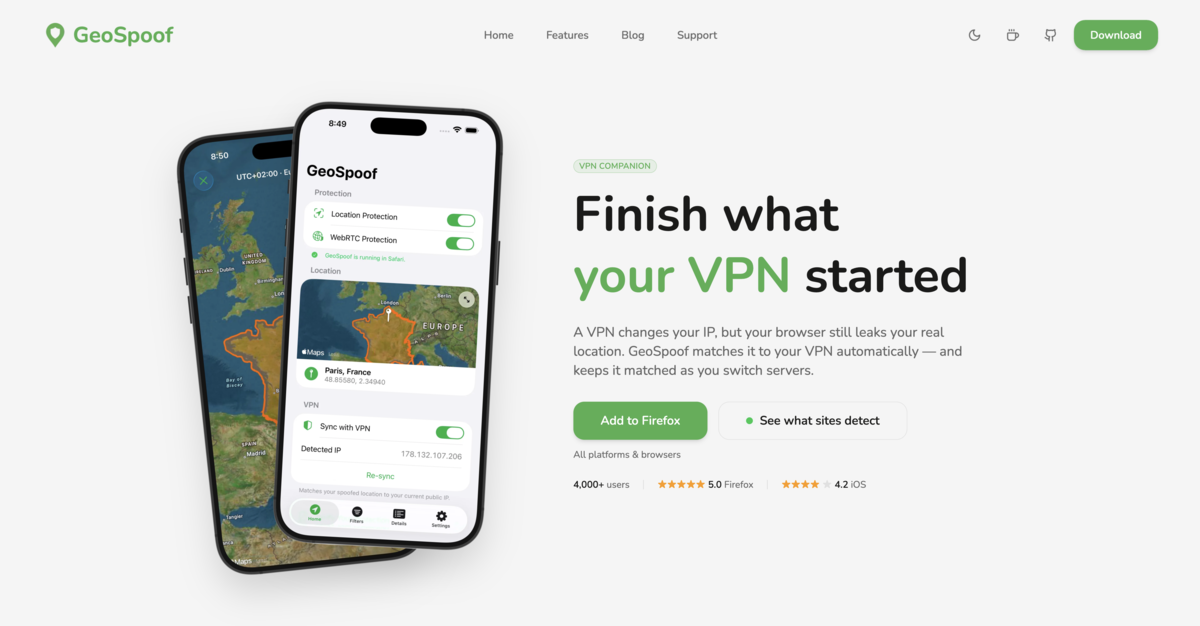
I started building GeoSpoof after I noticed my IP says one country, but the browser still hands sites my real location. Websites were flagging me because of this discrepancy. I searched for a good geolocation spoofer, only to go down a rabbit hole that there are dozens of signals that your browser emits and no tool could cover them all on every platform.
GeoSpoof overrides every location-related API to present one consistent signal for location. You can search a city, enter coordinates, or hit "Sync with VPN" to auto-detect your exit region and match it, which re-syncs when you switch servers. The overrides are disguised (Function.prototype.toString returns [native code], iframes patched on insert) so they survive the common fingerprinting checks.
Some examples of APIs covered: - Geolocation - Date - Temporal - EXSLT - Worker & Shared Worker (blob / data / URL scripts) - WebRTC - Deep engine-level spoofing on Chromium browsers with the CDP debugging api (opt-in)
It's cross-browser (Firefox, Chrome/Brave/Edge, Safari), available on mobile platforms as well (Android Firefox, iOS Safari), MIT licensed, with no backend or telemetry.
Source: https://github.com/anthonysgro/geospoof · Verify page: https://geospoof.com/verify
Happy to answer questions about it :)
Comments (0 of ) ⌛